Specialist agents, not one monolithic AI
Dozens of focused agents, each starting fresh with a scoped objective. No accumulated bias. No context collapse. When one agent finishes, another picks up the next attack vector.
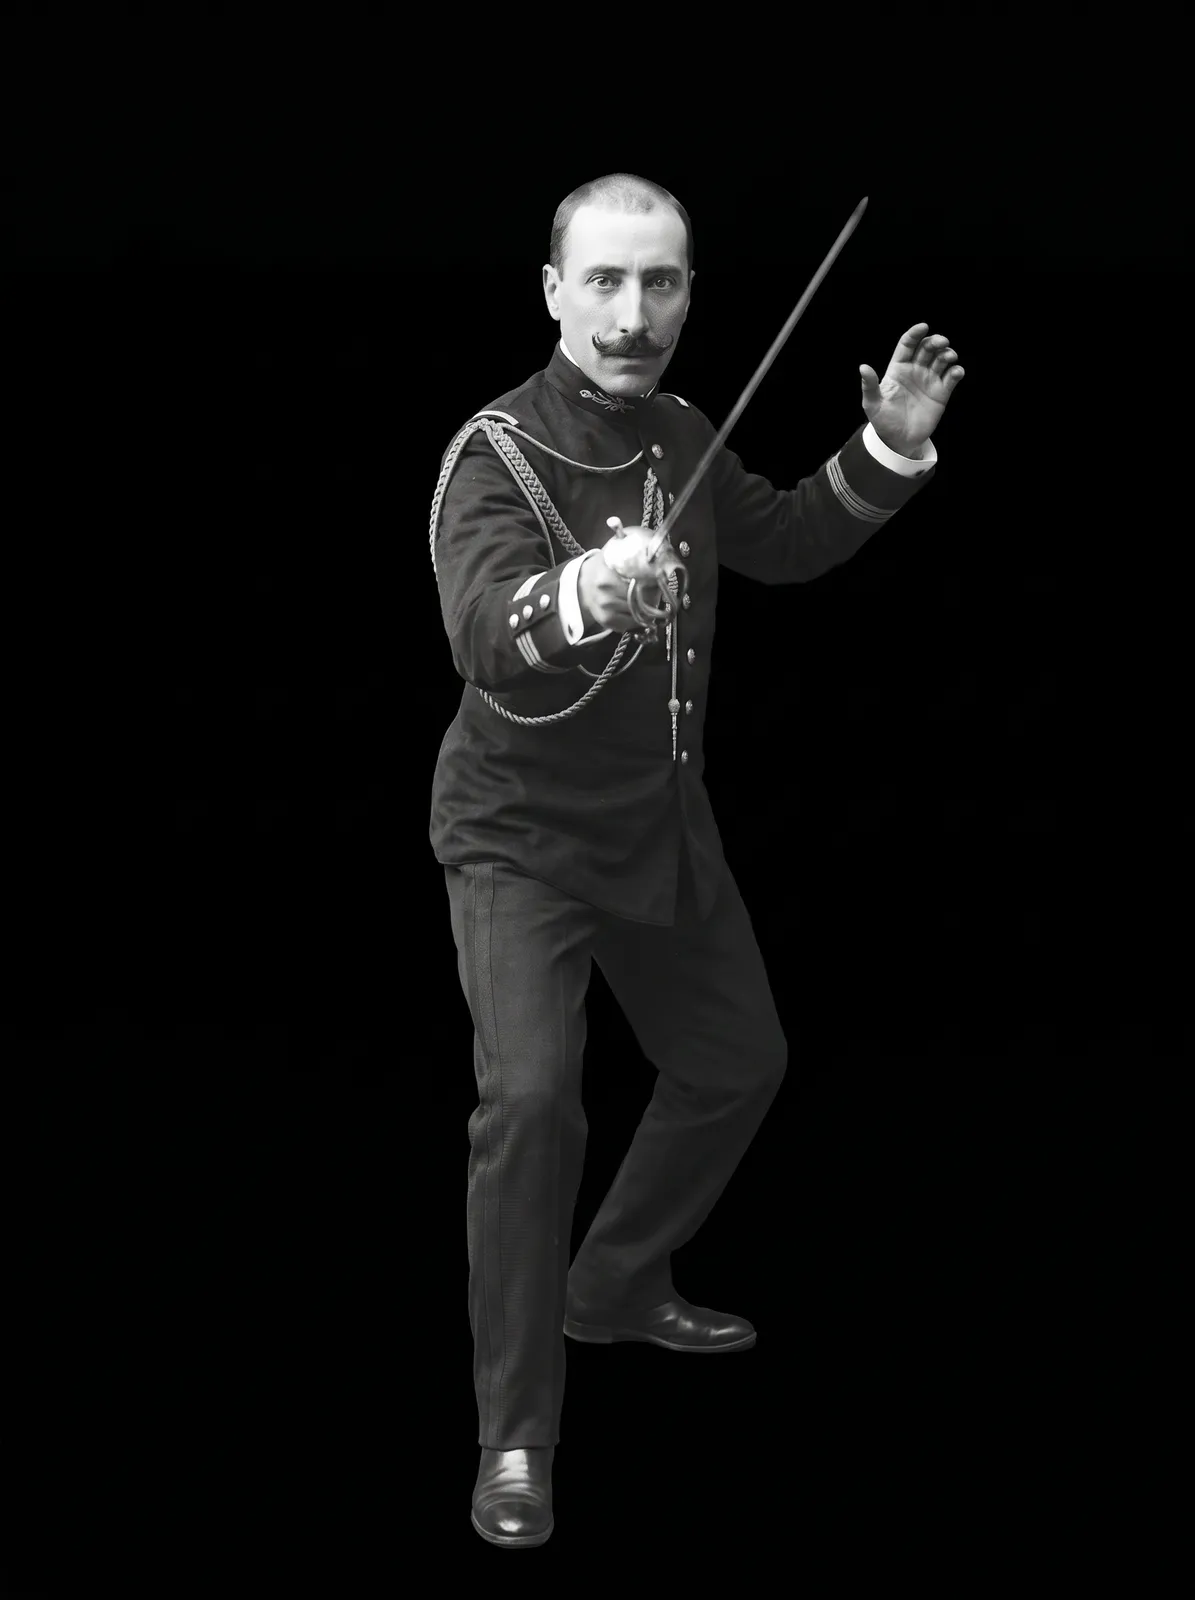
Émile is the orchestrator. He scopes the bout, sends specialist agents onto the piste and only counts the touches he can prove. Human-grade pentesting at machine speed.

Security tools flood teams with noise: more alerts, more triage, more wasted cycles. Fleuret operates on a different principle. AI agents explore attack paths creatively, but findings only surface when exploitability is confirmed through controlled validation. If a finding can't be proven with a PoC, it doesn't reach your report.
Émile doesn't follow a checklist. He coordinates dozens of specialist agents, each on one attack vector, and validates every finding before it reaches your team.
Define scope and launch
Targets, auth context, compliance framework. That is the piste. Émile never steps off it.
Map the attack surface
Émile sizes up the opponent: every endpoint, subdomain and entry point lands in the coverage graph.
Run multi-agent attacks
Auth bypass, injection chains, business logic, in parallel. Each agent retires after its mission.
Validate and report
A touch counts once a non-destructive PoC confirms it. Audit-ready PDF, DORA and NIS2 mapped.
Every move in plain terms: what Émile found, what he exploited, what he could not reach. The parries and the gaps go in your report too, so you know exactly what was tested.
Émile is a coordinated system of specialist agents, deterministic validators, and compliance-native reporting. Designed for production environments at scale.
The supervisor that maintains a global view of the engagement, tracks the Coverage Graph, and directs agents to untested surfaces. Applies deterministic logic to prioritize attack paths and decide when a pentest is complete.
Short-lived, focused agents that each target a specific attack vector: authentication, injection, IDOR, business logic. They operate in parallel and are retired after their mission to prevent accumulated bias.
Confirms whether a discovered issue is truly exploitable using controlled, production-safe challenges. Cuts false positives down by enforcing proof before any finding enters the report.
Tracks which endpoints, parameters, and auth contexts have been tested. The system of record for "is this pentest complete." Converts directly to exhaustiveness scores in the audit PDF.
Generates audit-ready output mapped to DORA, NIS2, ISO 27001, and SOC 2. PDF with reproducible PoCs, business impact, prioritized remediation, and offline verification.
7 CRITERIA · 3 PROVIDERS
FLEURET WINS 4 / 7
NOT A FIRM
Consulting firmTHE PLATFORM
FleuretNOT A SCANNER
Legacy scannerDepth
Depth
Depth
False positives
False positives
False positives
Speed
Speed
Speed
Cost
Cost
Cost
Frequency
Frequency
Frequency
Audit-grade report
Audit-grade report
Audit-grade report
Adaptability
Adaptability
Adaptability
Three design decisions that separate Fleuret from every other tool claiming AI security testing.
Dozens of focused agents, each starting fresh with a scoped objective. No accumulated bias. No context collapse. When one agent finishes, another picks up the next attack vector.
Findings ship with the actual, reproducible exploit as evidence. If it can't be proven, it doesn't reach your report. Proof before report is a design decision, not a target.
Scaleway France hosting. Open-weight models. Customer data never leaves Europe. Swap models when the frontier moves: the value is in the orchestration, not the model.
Fleuret runs against live systems. Three guarantees make that safe: nothing gets broken, everything is logged, every finding maps to a regulation your auditor recognizes.
Exploit validation uses controlled challenges that confirm exploitability without modifying data or disrupting systems. Your production stays untouched.
Every agent action is logged: who, what, when, from where. The audit trail ships with the PDF. Your compliance team can trace every finding to its source.
Report format maps directly to regulatory pentest requirements. Ed25519-signed PDF for offline verification. Board-deck export for quarterly risk reviews.